On August 15, 2023, Ransom Hub made headlines by releasing terabytes of sensitive data belonging to Australian organizations on the dark web, raising significant alarms regarding data security and privacy. This incident is not only illustrative of the severe repercussions of cyberattacks but also highlights the crucial necessity for robust external vulnerability scans.
Such scans play a vital role in identifying weaknesses in network defenses before malicious actors have the chance to exploit them. Implementing a thorough external vulnerability scan helps organizations proactively uncover potential weaknesses, fortify their security posture, and mitigate risks, ensuring that their defenses are resilient against ever-evolving cyber threats.
IT Company ensure compliance with industry standards while simultaneously protecting sensitive data from breaches, thereby maintaining trust with clients and stakeholders.
What is an External Vulnerability Scan?
An external vulnerability scan is a security assessment conducted on your network from an external perspective. It involves checking for weaknesses or vulnerabilities that could be exploited by malicious actors trying to gain unauthorized access. Unlike internal scans, which examine the security from within the network, external scans simulate potential attacks from outside sources.
Benefits of External Vulnerability Scans:
- Early Detection: By identifying vulnerabilities before they are exploited, you can prevent data breaches and other security incidents.
- Improved Security Posture: Regular scans help maintain and enhance your organization’s overall security defenses.
- Compliance: Many regulatory frameworks, including ISO 27001, require regular vulnerability assessments to ensure compliance.
- Cost-Effective: Detecting and addressing vulnerabilities early can save significant costs associated with data breaches and system downtimes.
Why are External Vulnerability Scans Important?
With increasing reliance on digital infrastructure, any security lapse can lead to severe reputational and financial consequences
Mitigating Risks with External Vulnerability Scans: What You Need to Know
In today’s interconnected digital landscape, ensuring the security of your systems and data is paramount. For IT managers, network security experts, system administrators, and website owners, understanding and implementing external vulnerability scans is crucial.
Identify System Weaknesses with External Vulnerability Scans:
An external vulnerability scan is a process that uses automated tools to identify potential vulnerabilities in your systems from an outsider’s perspective. It simulates the actions of a hacker attempting to exploit weaknesses, helping you preemptively address these vulnerabilities before they can be exploited.
Secure Your Network: The Importance of Early Detection
- Proactive Security Measures: By identifying vulnerabilities before they are exploited, you can take proactive steps to secure your network.
- Compliance: Regular scans can help you comply with industry regulations and standards, such as ISO 27001, which emphasizes risk management and information security.
- Reputation Management: Preventing security breaches protects your organization’s reputation and maintains customer trust.
- Cost Savings: Addressing potential vulnerabilities early can save your organization significant resources by avoiding costly breaches and downtime.
Align Security Measures with ISO 27001 Standards:
External vulnerability scans are crucial because they provide a hacker’s-eye view of your network. They help you:
- Prioritize security efforts by highlighting the most critical vulnerabilities.
- Ensure the consistency of your security measures across different network segments.
- Support your risk management framework, aligning with standards like ISO 27001.
How to Implement External Vulnerability Scans?
- Set Clear Objectives: Define what you want to achieve with your scans, whether it’s compliance, enhanced security, or risk assessment.
- Choose the Right Tools: Select vulnerability scanning tools that align with your organization’s size, industry, and security requirements.
- Schedule Regular Scans: Establish a regular schedule for conducting scans, ensuring ongoing security vigilance.
- Analyze Results: Review scan results carefully to understand the vulnerabilities detected and their potential impact.
- Address Vulnerabilities: Develop a plan to remediate identified vulnerabilities, prioritizing them based on risk level and impact.
- Document and Review: Keep detailed records of scans and remediation efforts, and regularly review them to enhance your security posture.
Types of External Vulnerability Scans:
- Network-Based Scans: These scans examine your network infrastructure to identify weak spots, such as outdated software or misconfigured systems.
- Web Application Scans: Focused on identifying vulnerabilities in web applications, these scans check for issues like SQL injection and cross-site scripting (XSS).
- Cloud-Based Scans: Tailored for cloud environments, these scans address vulnerabilities specific to cloud platforms and services.
Process and Methodology:
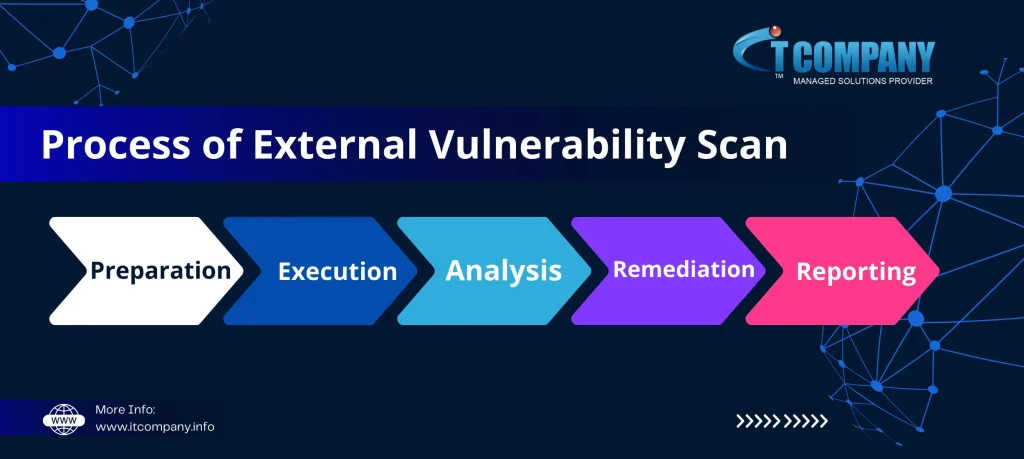
Preparation:
- Define the scope and objectives.
- Gather necessary permissions and approvals.
Execution:
- Use automated tools to conduct the scan
- Monitor the scanning process for any anomalies
Analysis:
- Evaluate scan results to assess the severity and impact of vulnerabilities.
- Prioritize vulnerabilities based on risk and potential impact on the organization.
Remediation:
- Implement corrective measures to address identified vulnerabilities.
- Validate remediation efforts through follow-up scans.
Reporting:
- Generate comprehensive reports detailing the vulnerabilities and remediation efforts.
- Share findings with relevant stakeholders to ensure awareness and accountability.
Industry Standards and Best Practices:
Adhering to industry standards, such as ISO 27001, is essential for effective risk management and information security. Consider these best practices:
- Regular Updates: Keep scanning tools and systems up to date to ensure they detect the latest vulnerabilities.
- Comprehensive Coverage: Ensure all network segments and systems are included in the scan.
- Continuous Monitoring: Complement periodic scans with continuous monitoring solutions for real-time threat detection.
- Training and Awareness: Educate your team about security best practices to build a culture of vigilance and responsiveness.
Final Thoughts
By implementing external vulnerability scans, you equip your organization to stay a step ahead of potential threats, safeguarding your systems and data. Ready to enhance your security posture? Start integrating regular scans into your risk management strategy today.