A fraudulent business email does not need poor spelling, an unknown sender or an obvious malware attachment to cause damage. It may resemble an ordinary supplier invoice, use familiar language, and arrive as part of an existing conversation. The only unusual detail could be a request to use different bank information.
Introduction
Email security with real-time threat detection in Australia combines message filtering, phishing and impersonation detection, link and attachment analysis, account monitoring and incident response to reduce email-based business risk. For Australian businesses, modern email protection needs to consider four connected elements:
- Message
- Identity
- Action
- Response
A security product may detect a suspicious message, but the final outcome also depends on whether the user account is secure, what action the employee takes and who owns the investigation. Businesses assessing their existing protection can compare these requirements with IT Company Australia’s email security solutions.
What Is Real-Time Email Threat Detection?
Real-time email threat detection refers to technologies and processes that identify suspicious activity close to the point at which a message, attachment, URL or account event occurs. It can include message inspection before delivery, URL analysis when a link is used, attachment scanning, post-delivery reassessment, account monitoring, and security investigation. However, real-time does not describe one universal service level. Depending on the platform, it may involve pre-delivery inspection, link analysis at the time of use, post-delivery detection, or near-real-time investigation. Businesses should confirm which events are analysed, how quickly alerts appear, and whether automated or human response is included. Microsoft illustrates the distinction clearly. Its Defender for Office 365 documentation describes Threat Explorer and Real-time detections as near-real-time reporting and investigation tools. Microsoft states that Real-time detection is available with Defender for Office 365 Plan 1, while Threat Explorer is available with Plan 2 and adds further investigation capabilities.
Real-time email protection can happen at different stages
Detection without ownership is an alert, not an incident response.
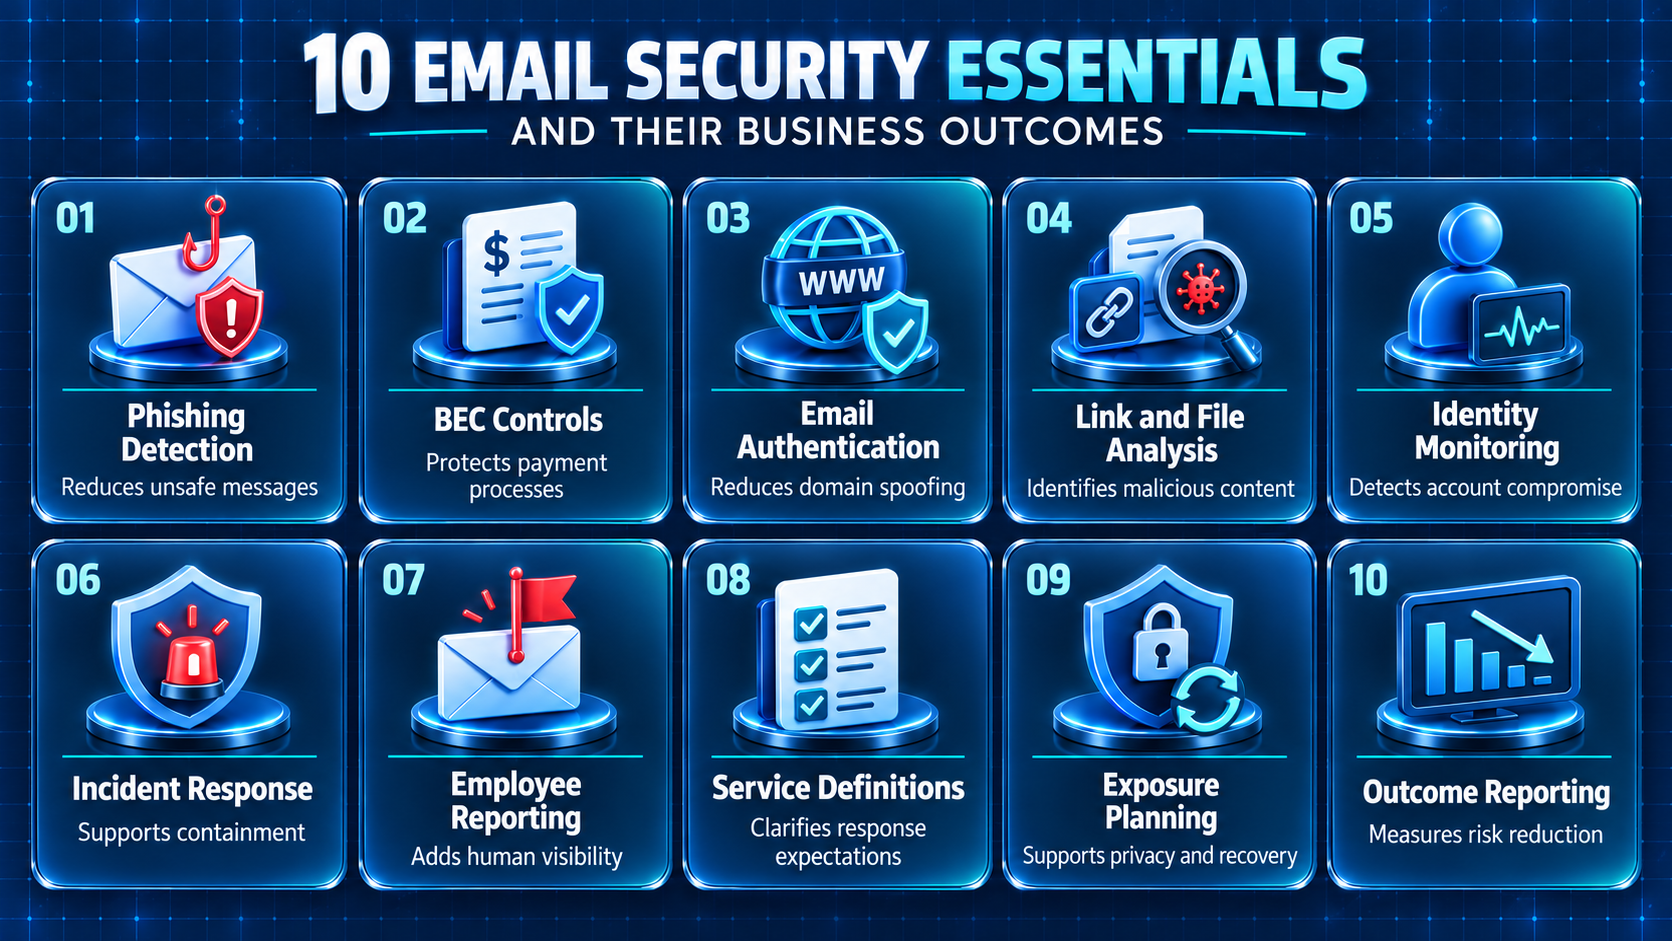
Email Security Essentials at a Glance
Why Email Security Matters for Australian Businesses
Email connects many of the processes attackers value most: invoices, payroll, customer information, cloud accounts, password resets and supplier communication. Scamwatch warns that business email compromise commonly involves criminals impersonating a business and sending invoices containing changed payment information. Its guidance advises businesses to stop and independently verify changes to payee details using a trusted contact method. The Australian Signals Directorate also recommends controls specifically aimed at preventing business email compromise and spoofing. For Australian SMEs, email security therefore has four practical objectives:
- Protect money
- Protect identities
- Protect information
- Protect trust in normal communication
10 Essentials of Email Security with Real-Time Threat Detection in Australia
Detect Phishing Before It Becomes Credential Theft
Phishing aims to persuade someone to complete an unsafe action. A message may claim that a Microsoft 365 password is expiring; a document requires authentication, or an employee needs to verify an account urgently. Modern filtering can evaluate sender characteristics, links, attachments, known threat indicators and message patterns before employees have to make every security judgement themselves. The objective here is specifically credential theft and unsafe user action, not every other type of email fraud. For Microsoft environments, the guide Setup Protection for Maximum Email Security in Office 365 explains controls including Safe Links, Safe Attachments, anti-phishing policies, and MFA. Scamwatch’s current email-scam guidance also warns Australians about messages containing links or attachments requesting login details or personal information.
Treat Business Email Compromise as Financial-Process Risk
Business email compromise deserves its own category because the objective is often not to steal a password; it is to manipulate an existing business process. An attacker may impersonate a supplier, executive or employee and request a payment, invoice of change or transfer. This means technology cannot provide the entire defense.
A stronger payment process is:
Change requested → independently verify → approve → pay
Scamwatch advises businesses to check changed payee information and contact the organisation using a phone number sourced independently rather than relying on details in the suspicious email. That separates BEC protection from general phishing detection: email security identifies risk; business controls help prevent the financial action.
Authenticate Email With SPF, DKIM and DMARC
Sender authenticity is another distinct security problem. The Australian Signals Directorate recommends discussing three email-authentication protocols with email and DNS providers:
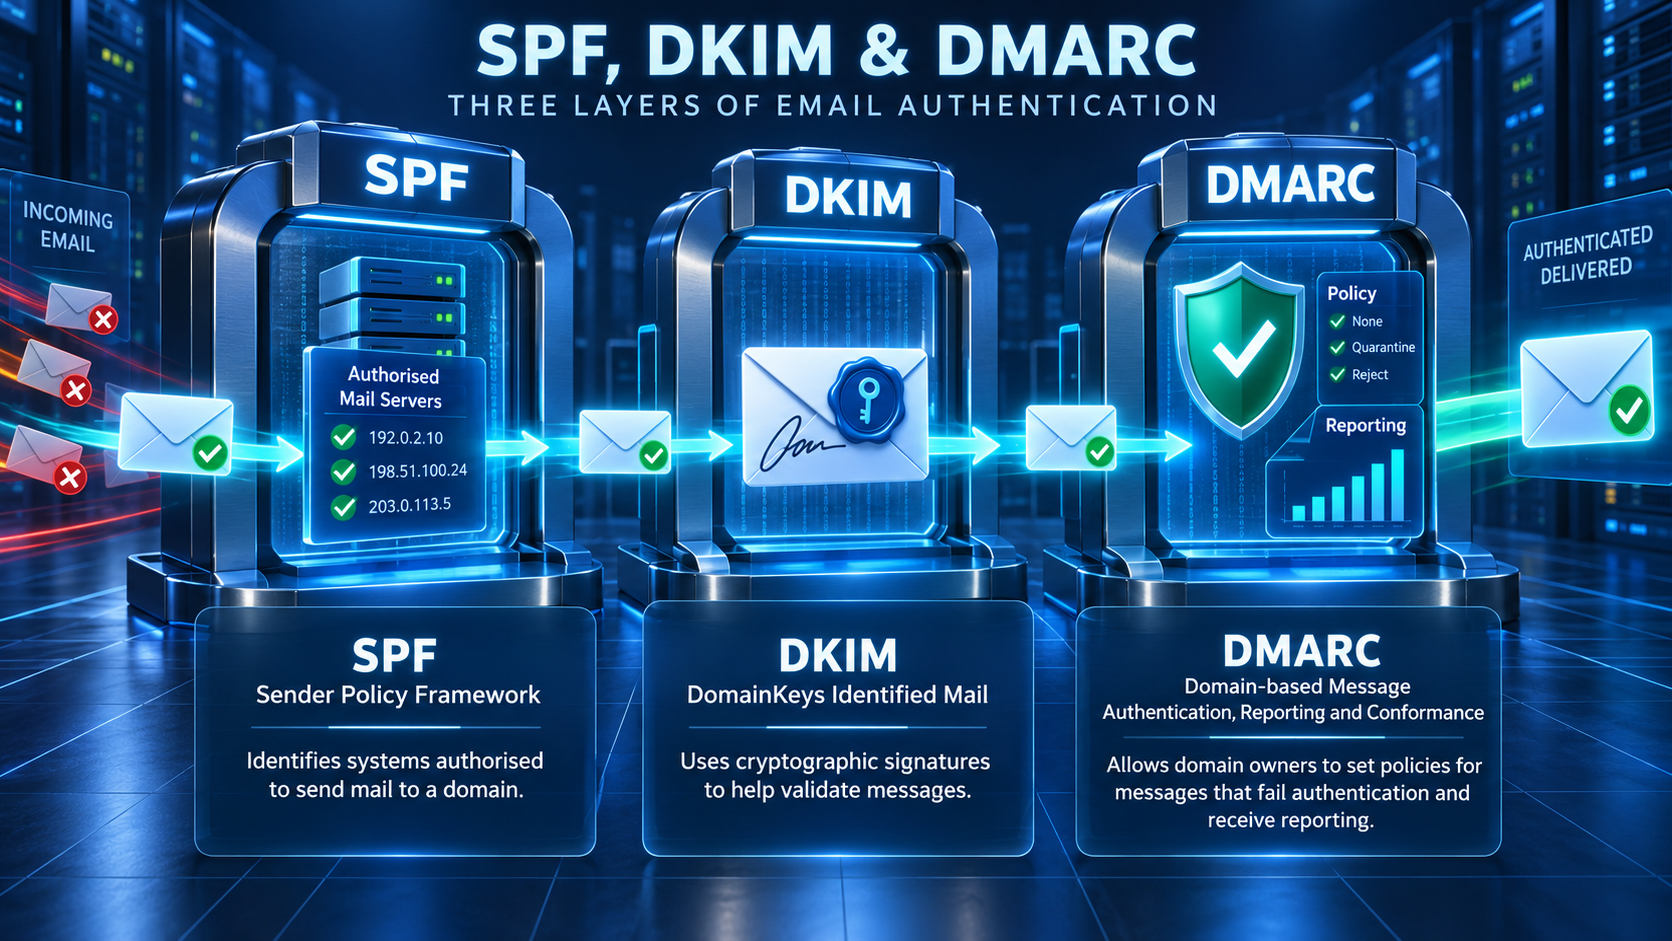
ASD specifically identifies SPF, DKIM and DMARC as measures businesses can use to combat spoofed email. Their limits matter just as much.
SPF, DKIM, and DMARC can help authenticate legitimate email and reduce direct domain spoofing. However, they do not prevent every display-name attack, lookalike domain, or message sent from a genuinely compromised account. Authentication should therefore be treated as one layer within the wider email security model.
Analyse Links and Attachments as Content Risks
A sender can appear trustworthy while the content is dangerous. That may happen because a genuine account has been compromised or because a malicious URL or attachment is embedded in a convincing message. Content inspection therefore has a different purpose from sender authentication. Depending on the platform and licensing, protection may include URL reputation analysis, clicking information, attachment scanning, file analysis, or sandboxing. Microsoft documents malware, phishing, content-malware and URL-click information within its Defender for Office 365 investigation tools, although capabilities differ between Real-time detections and Threat Explorer. Businesses operating Microsoft environments should compare their actual requirements and licensing rather than assuming every Microsoft 365 subscription provides the same security capabilities. Relevant platform information is available through Microsoft 365 services.
Connect Email Detection With Identity Monitoring
The security problem changes significantly once an attacker obtains legitimate access. A compromised account may be used to read messages, create forwarding rules, contact suppliers, or target other employees. At that stage, incoming email filtering alone cannot resolve the incident. Organisations may need to investigate unusual sign-ins, unexpected mailbox settings, suspicious permissions, authentication activity, and messages sent after the suspected compromise. The related article How Spam Emails Can Lead to Cloud Account Compromise explains how malicious messages can lead to broader exposure when one identity connects to email, file storage, collaboration tools, and other cloud services.
Build Email Protection into a Wider Cybersecurity Model
A suspicious message may be only the first visible sign of a larger incident. A practical response model is:
Detect → Investigate → Contain → Recover → Review
If an employee enters credentials into a fraudulent website, removing the original email does not contain the compromise. The organisation may also need to secure the user’s account, revoke sessions, inspect activity, and determine whether information or other systems were affected. Microsoft’s Defender tooling supports investigation of delivered malicious email and actions such as finding or deleting messages and examining sender information. Australian businesses with wider monitoring requirements can consider how email protection connects with managed cyber security services.
Information-security governance
Email frequently contains financial records, customer information, and commercially sensitive communications. IT Company Australia operates an ISO/IEC 27001:2022-certified information security management system, providing a recognised governance framework for information-security risks within its certified scope. Its current About page identifies that certification. Certification should remain one input into supplier due to diligence. It does not guarantee that incidents cannot occur or make a customer’s environment automatically compliant.
Make Employee Reporting Part of Detection
Technology cannot understand every business context.
An employee may know immediately that a supplier never requests bank changes by email or that a manager is away and could not have sent an urgent request. That makes employees have another useful detection layer. The reporting mechanism should be simple, but the responsibility should shift away from the employee once a suspicious email is reported. The next step may involve an internal IT team, security team, or external support provider. Where organisations want user support and incident escalation connected, broader managed IT services may provide the operational framework. Employees should report. They should not be expected to investigate.
Define “Real-Time”, Response and Support Separately
This is one of the most important buying criteria. A provider can truthfully describe an automated scanning technology as real-time even if human investigation operates according to completely different service hours. Businesses should therefore separate detection from response. Microsoft’s own terminology reinforces this point: despite the product name “Real-time detections”, Microsoft describes its Explorer and Real-time detections tools as near-real-time reporting and investigation capabilities.
Prepare for Data Exposure and Recovery
A compromised mailbox can contain far more than individual messages. It may expose customer conversations, invoices, attachments, confidential documents, or password-reset information. The response plan should establish who investigates the account, what evidence is retained, how other affected systems are checked, and who owns business communications. Recovery also requires its own planning. Email hosted in the cloud does not automatically mean every recovery or retention requirement has been addressed. Businesses with defined recovery requirements should assess cloud backup services separately from their email security configuration. The goal is to prepare for the possibility that prevention fails not to assume that every message will always be stopped.
Measure Outcomes, Not Just Blocked Messages
A dashboard reporting 50,000 blocked spam messages sounds impressive. It does not necessarily tell management whether meaningful business risk is decreasing. More useful measures can include confirmed phishing attempts, BEC cases, impersonation events, malicious links and files, compromised accounts, user-reported threats, investigation time and containment time.
This shifts email security from inbox housekeeping to measurable risk management.
How Much Does Email Security Cost in Australia?
Email security costs vary because each business has different users, platforms and protection needs. The number of accounts and required licences also affects the price. Basic spam filtering generally costs less than advanced services that scan links, analyse attachments and monitor account activity. Managed investigation and incident response can increase the total fee. Businesses should compare the full scope, exclusions and support hours instead of considering only the advertised price.
Current pricing example
At the time of review, IT Company Australia’s live Email Security page displayed Email Security & Protection at AUD 36.94 per month, alongside discounted longer-term options. The page lists advanced spam filtering, virus and malware blocking, continuous updates, spam management, unlimited email protection, and DoS protection.
Basic Filtering vs More Complete Managed Email Security
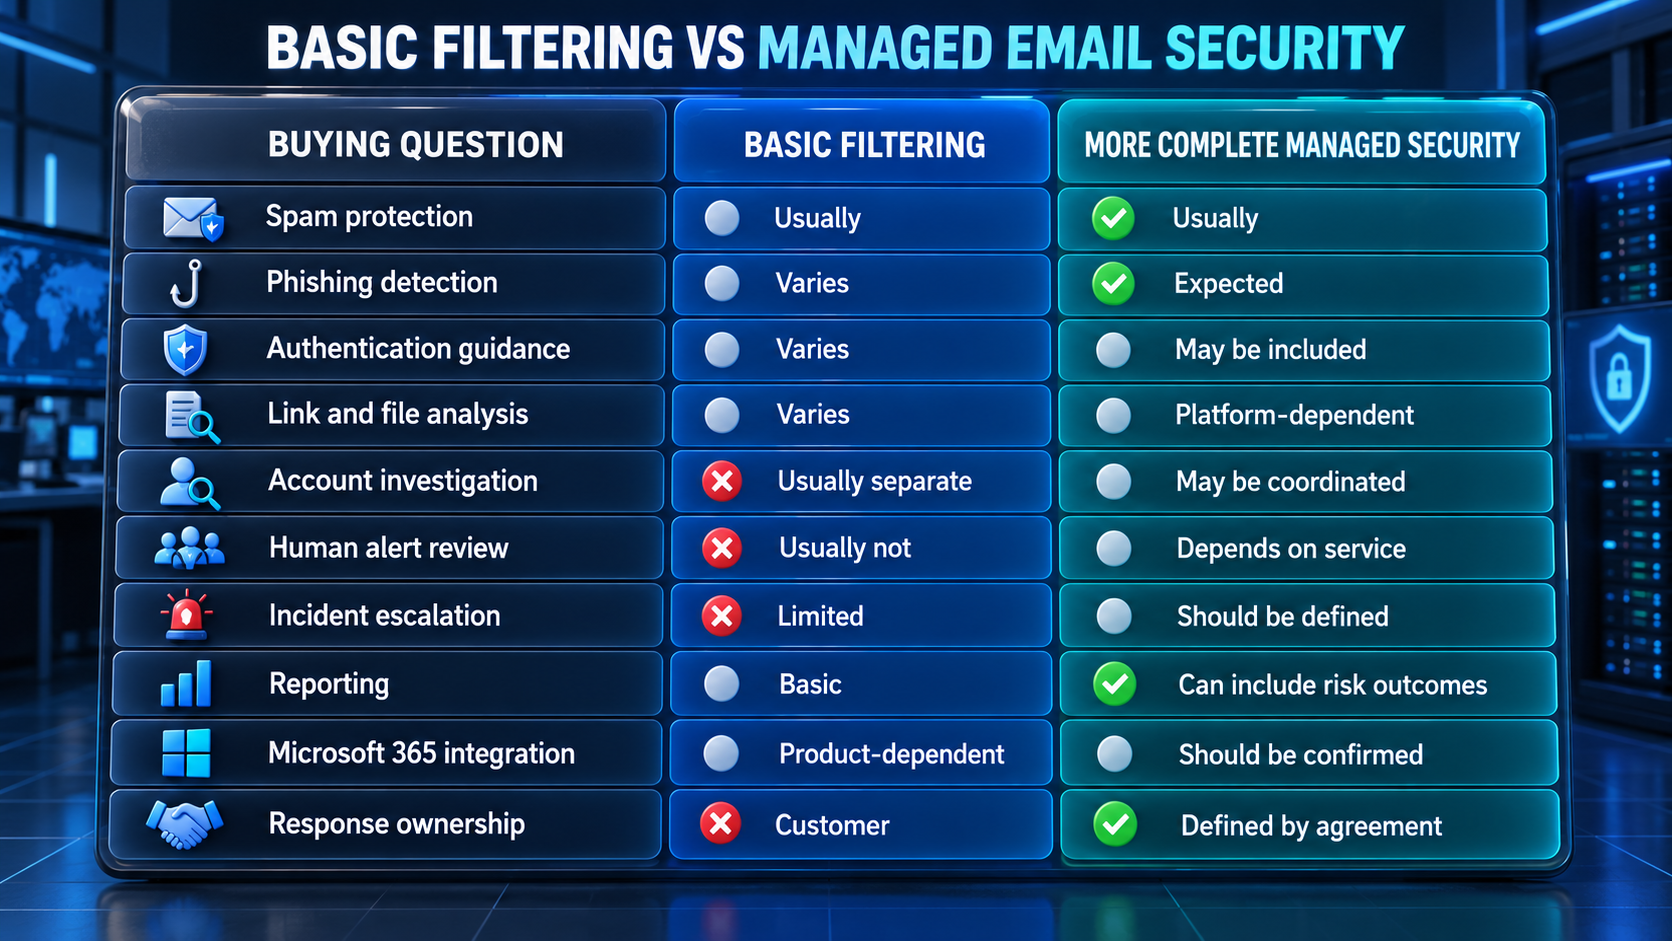
The best option is not automatically the one with the most features.
An Australian SME needs controls that match its email platform, risk profile, internal capability and response expectations.
Why Managed Email Security Can Matter for an Australian SME
Basic filtering may be enough for a simple environment where the organisation has sufficient internal capability to investigate suspicious activity itself. Managed email security becomes more useful when an SME needs someone to coordinate detection, account investigation, Microsoft 365 administration, employee support, and escalation. The difference can be illustrated with one question:
If a genuine email threat is detected tomorrow morning, who owns the next step?
If nobody can answer that clearly, the business may have filtered but not a complete operational response model.
Email Security Support Across Australia
Australian organisations increasingly operate across offices, remote teams and multiple time zones. Local intent therefore matters most when it reflects how employees actually receive support not when city names are inserted merely for search engines. Businesses should compare whether a provider can support users across their operating locations, maintain consistent security policies, and coordinate incidents when several offices are involved.
Email Security with Real-Time Threat Detection in Sydney
Businesses evaluating email security with real-time threat detection in Sydney should consider detection capability alongside response ownership, Microsoft 365 integration, account monitoring and escalation procedures. Organisations looking for ITCompany Sydney support can review the relevant Sydney contact pathway and assess whether email-security incidents can be coordinated effectively when a suspicious message develops into an account, user or wider cloud-security issue. For Sydney-based businesses, the key question is not only whether threats are detected, but also who investigates, who communicates with affected users, and how quickly the incident is escalated when further action is required.
Email Security with Real-Time Threat Detection in Melbourne
Businesses looking for ITCompany Melbourne support should assess phishing protection, email authentication, account monitoring, Microsoft 365 integration, incident escalation and response responsibilities as part of their email-security strategy.
Email Security with Real-Time Threat Detection in Brisbane
Organisations seeking ITCompany Brisbane support should look beyond basic spam filtering and consider how suspicious accounts, fraudulent payment requests, malicious links and employee-reported threats are investigated and escalated.
Email Security with Real-Time Threat Detection in Perth
Businesses considering ITCompany Perth should also review support availability, escalation timing and incident coordination, particularly when employees operate across different locations or Australian time zones.
Why IT Company Australia May Fit Some Requirements
Email threats can move quickly from the inbox into Microsoft 365 identities, cloud services, user support, and recovery. IT Company Australia’s service catalogue includes email security, Microsoft 365, managed cyber security, managed IT and cloud backup, which can reduce hand-offs when one incident crosses several technical areas. Its current Email Security & Protection page includes filtering, malware protection, continuous updates, and additional email protection controls.
That scope should still be assessed using the same criteria as any alternative: threat coverage, licensing, integrations, automated action, human response, service hours, reporting, exclusions, and total cost. Businesses ready to move from education into service comparison can review email security solutions for Australian businesses.
Frequently Asked Questions
What is email security with real-time threat detection in Australia?
Email security with real-time threat detection in Australia combines filtering, phishing and impersonation detection, link and attachment analysis, identity monitoring and incident-response processes to reduce email-related business risk.
Does real-time email security mean an analyst responds immediately?
No. Real-time may describe automated inspection rather than human response. Some investigation tools operate in near real time, while human action may follow separate service targets. Microsoft explicitly describes Threat Explorer and Real-time detections as near-real-time tools.
What is a business email compromise?
Business email compromise is fraud that manipulates trusted business communication. Criminals may impersonate a supplier or use a compromised account to redirect payments or obtain information. Scamwatch advises businesses to independently verify changed payment information.
Do SPF, DKIM and DMARC stop all email impersonation?
No. They help authenticate legitimate email and reduce direct domain spoofing, but they cannot prevent every display-name attack, lookalike-domain scam or message sent from an already-compromised account. ASD recommends the three controls as part of business email protection.
Does Microsoft 365 include real-time email threat detection?
Capabilities depend on licensing. Microsoft states that Real-time detection is available with Defender for Office 365 Plan 1, while Threat Explorer is available with Plan 2 and provides additional investigation capabilities.
How much does email security cost in Australia?
Pricing varies according to platform, users, features, monitoring, and support. At the time of review on 9 September 2026, IT Company Australia’s live page displayed Email Security & Protection at AUD 36.94 per month, with discounted longer-term options advertised.
What should happen after an employee reports a suspicious email?
The report should enter a defined review and escalation process. If compromise is suspected, the investigation may need to cover the mailbox, authentication sessions, other recipients, payment activity and potentially affected information.
Final Thoughts
Email attacks increasingly succeed by looking ordinary. A message may contain no obvious malware and still manipulate an employee, impersonate a trusted supplier or lead to account compromise. That is why email security with real-time threat detection in Australia should be assessed across four connected areas:
Message → Identity → Action → Response
Ask what happens before delivery; what can be detected afterwards, whether links and attachments are reassessed, how account activity is investigated and—most importantly who acts when something is found.
Detection without ownership is an alert, not an incident response.
Businesses that want to compare phishing protection, spoofing controls, link and attachment analysis, Microsoft 365 integration and response responsibilities can review IT Company Australia’s email security solutions and request a scope based on their users, email platform and security requirements.
